UNI at Ecomondo 2026: the new EN standards on the Digital Product Passport aren't a separate project if you already have an ISMS
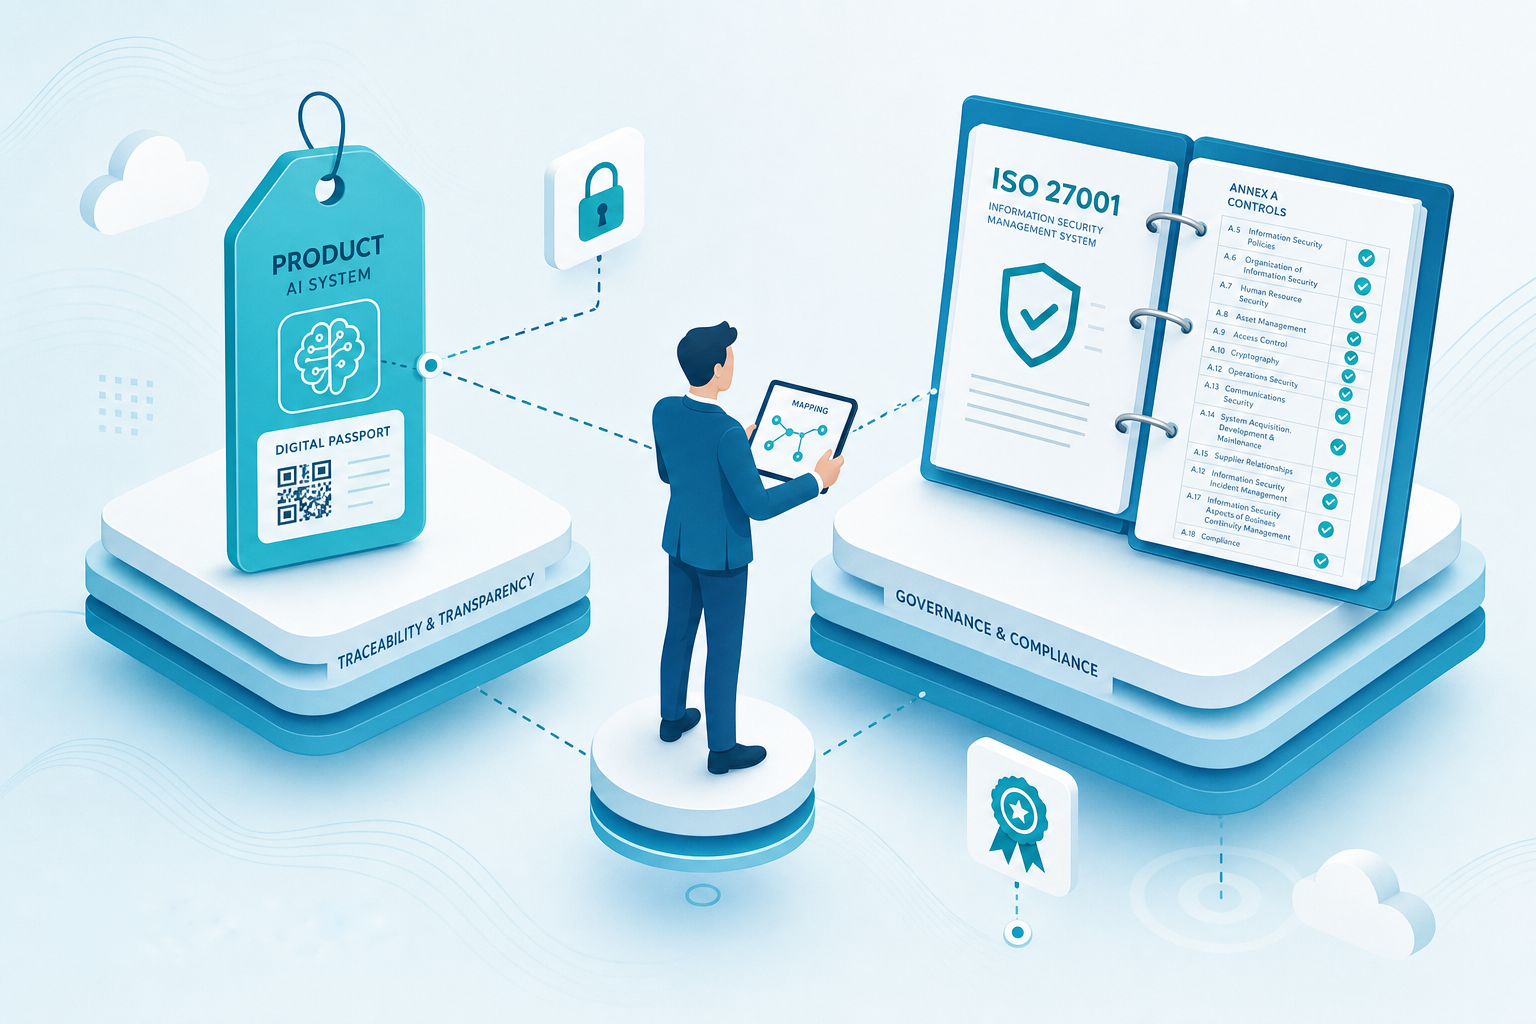
UNI (Italy's national standardization body, a member of CEN and CENELEC) is taking part in Ecomondo 2026 (Rimini, 3-6 November) with an event on the Digital Product Passport (DPP, mandated by the EU Ecodesign regulation), scheduled for 3 November as part of the European project bi0space: it runs in English, with registration via an online form — worth knowing if you need to organize your team's attendance. The occasion comes right after CEN and CENELEC (the European standardization bodies) published two new technical standards on the topic. If your organization already has a certified ISMS (Information Security Management System) under ISO 27001, you're not starting from zero: the question is what you already cover and what's missing.
What the Digital Product Passport is, and why the technical standard arrives only now
The DPP originates from the ESPR (Ecodesign for Sustainable Products Regulation, Regulation (EU) 2024/1781), in force since 18 July 2024: it states that a product can only be placed on the market with a compliant DPP, but only for product categories progressively identified through Commission delegated acts — it is not, today, a blanket obligation for all companies. The ESPR work plan lists among its priority categories iron and steel, aluminium, textiles and footwear, furniture and mattresses, tyres, detergents, paints, lubricants, chemicals, energy-related products, and ICT and electronics: if you operate in one of these sectors, the DPP isn't a remote hypothesis but an obligation that will arrive through a delegated act specific to your category. Once the regulation set the "what," it fell to CEN and CENELEC — of which UNI is the Italian member — to standardize the "how": the first 6 harmonized DPP standards had already been adopted by UNI in July 2026; the two discussed here are a second package, a sign that the standardization work continues in successive phases and didn't stop with the first group of standards.
The two new standards: EN 18239:2026 and EN 18246:2026
CEN and CENELEC have published — not merely announced — EN 18239:2026, "Digital Product Passport – Access rights management, information system security, and business confidentiality," and EN 18246:2026, "Digital Product Passport – Data authentication, reliability and integrity." The first covers access management, information security and business confidentiality of the data held in the DPP — relevant if you're worried about exposing sensitive supply-chain data alongside mandatory information. The second focuses on data authentication and integrity: ensuring the passport's information hasn't been altered along the chain from manufacturer to consumer or recycler. The fact that both are already published, not merely announced or under public enquiry, changes the planning horizon: these aren't future standards to keep an eye on, but technical references already available to purchase and consult to start the mapping work.
Where it overlaps with ISO 27001 (and where it doesn't)
On the page announcing the event, UNI does not state any explicit link between the two standards and ISO/IEC 27001 Annex A controls: what follows is Tomato's own editorial reading, not a claim made by the source. That said, access management, authentication and data integrity are areas a mature ISO 27001 ISMS already governs, so a good share of what EN 18239 and EN 18246 require may already exist in your organization. In practice, a mature ISO 27001 ISMS already includes access control policies, authentication procedures and mechanisms to ensure the integrity of the data it handles — exactly the three areas named in the titles of the two new standards. This doesn't mean ISO 27001 certification automatically "covers" the DPP — no source claims that, and neither do we — but that the starting point for a gap analysis isn't a blank page. What a generic ISMS doesn't automatically cover is supply-chain traceability and the product-specific data management that the DPP requires, which remains a distinct scope.
What to do if you already have a certified ISMS
If you already have a certified ISO 27001 ISMS, the sensible move isn't to launch a separate DPP project, but a targeted gap analysis: map which Annex A controls already cover access, authentication and data integrity, and isolate only what's specific to the product passport. It's work you can start right now, regardless of the formal adoption status of the work plan or whether the registry is up and running: mapping your existing Annex A controls doesn't depend on any delegated act — it's an internal exercise you can run on your ISMS as it stands, so you're ready once the standard becomes mandatory for your category. Waiting for official adoption only postpones work with no external prerequisite. On timing, though, caution is warranted: the concrete obligation kicks in product by product through delegated acts; the Commission's first work plan was due by 19 April 2025 (ICT and electronics among the priority categories) and the DPP registry by 19 July 2026, but this article has not verified whether these were actually adopted: treat them as statutory deadlines, not confirmed facts.
What to do now
Three questions to orient yourselves: does your product category fall among the ESPR work plan's priorities (iron and steel, textiles, ICT and electronics, among others)? Does your ISO 27001 ISMS already document coverage of access, authentication and data integrity for the products you handle? Have you already distinguished, within your management system, what counts as general information security versus what the DPP will specifically require?
If you can't confidently answer these questions, it's time to assess the maturity of your management system before the DPP becomes mandatory for your product category: Assess the maturity of your management system — ISO/IEC 27001 ISMS. For the broader 2026 ISO picture, see also ISO/IEC 27000:2026: what actually changes.
Sources
- UNI — UNI ad Ecomondo 2026: il Digital Product Passport e l’economia circolare — pubblicata il 30 settembre 2026
- UNI — Digital Product Passport: pubblicate due nuove norme da CEN e CENELEC
- EN 18239:2026 — Access rights management, information system security, and business confidentiality
- EN 18246:2026 — Data authentication, reliability and integrity