Blog
Insights, guides and news from the compliance and RegTech world
Explosive Prompts: CERT-AGID measures the prompt injection that waits for the right moment
CERT-AGID measures delayed-effect prompt injection on 4 models: with an authorization control outside the model, executed actions dropped to zero.
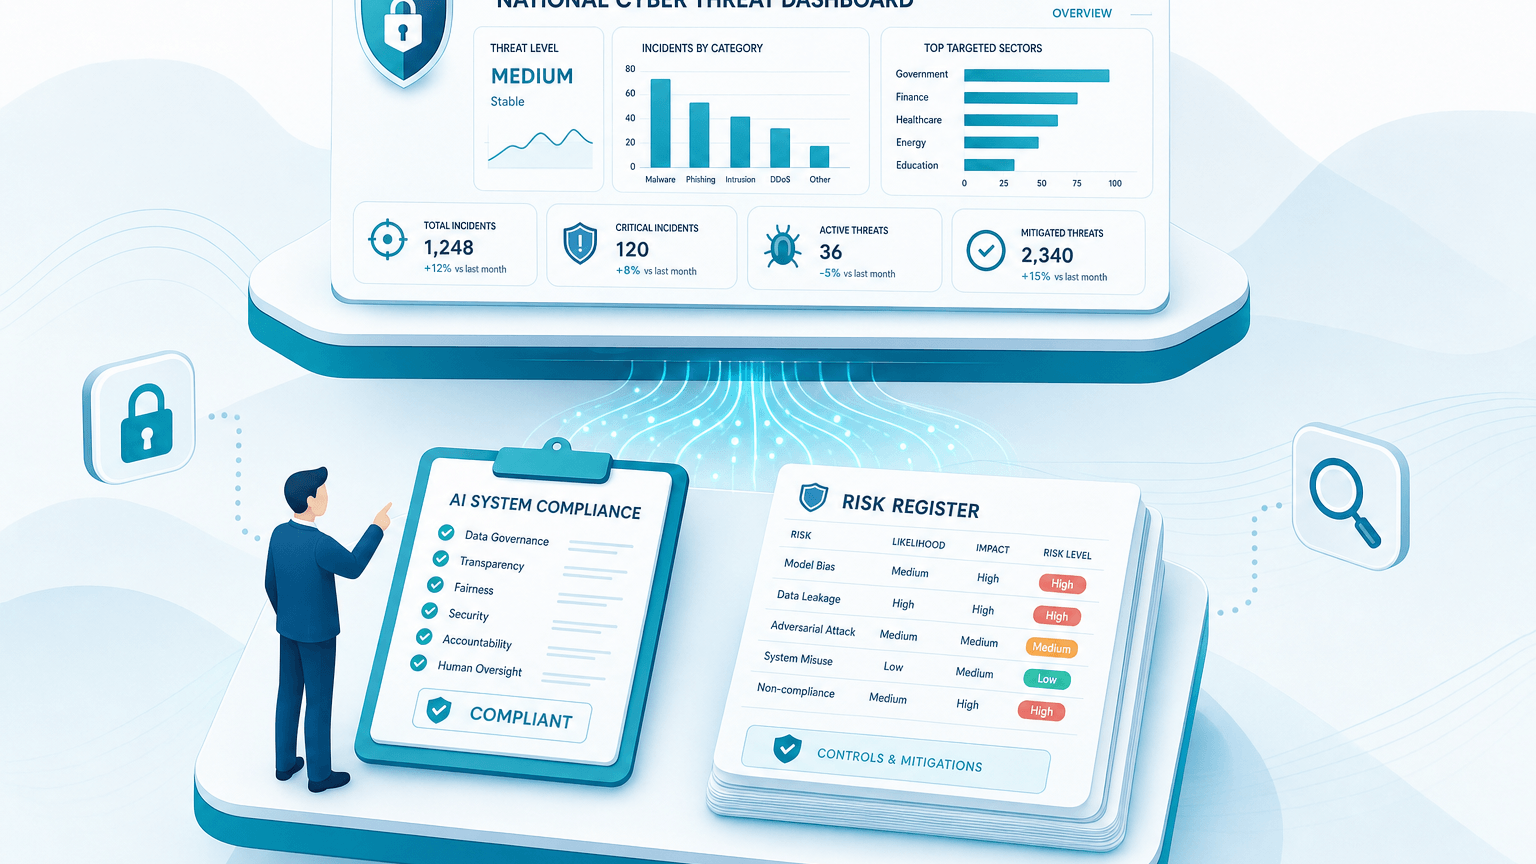
ACN Operational Summary, August 2026: turning national cyber threat data into NIS2 risk assessment input
ACN published its latest Operational Summary with cyber threat data for Italy (August 2026): here's how to feed it into your NIS2/ISO 27001 risk register.
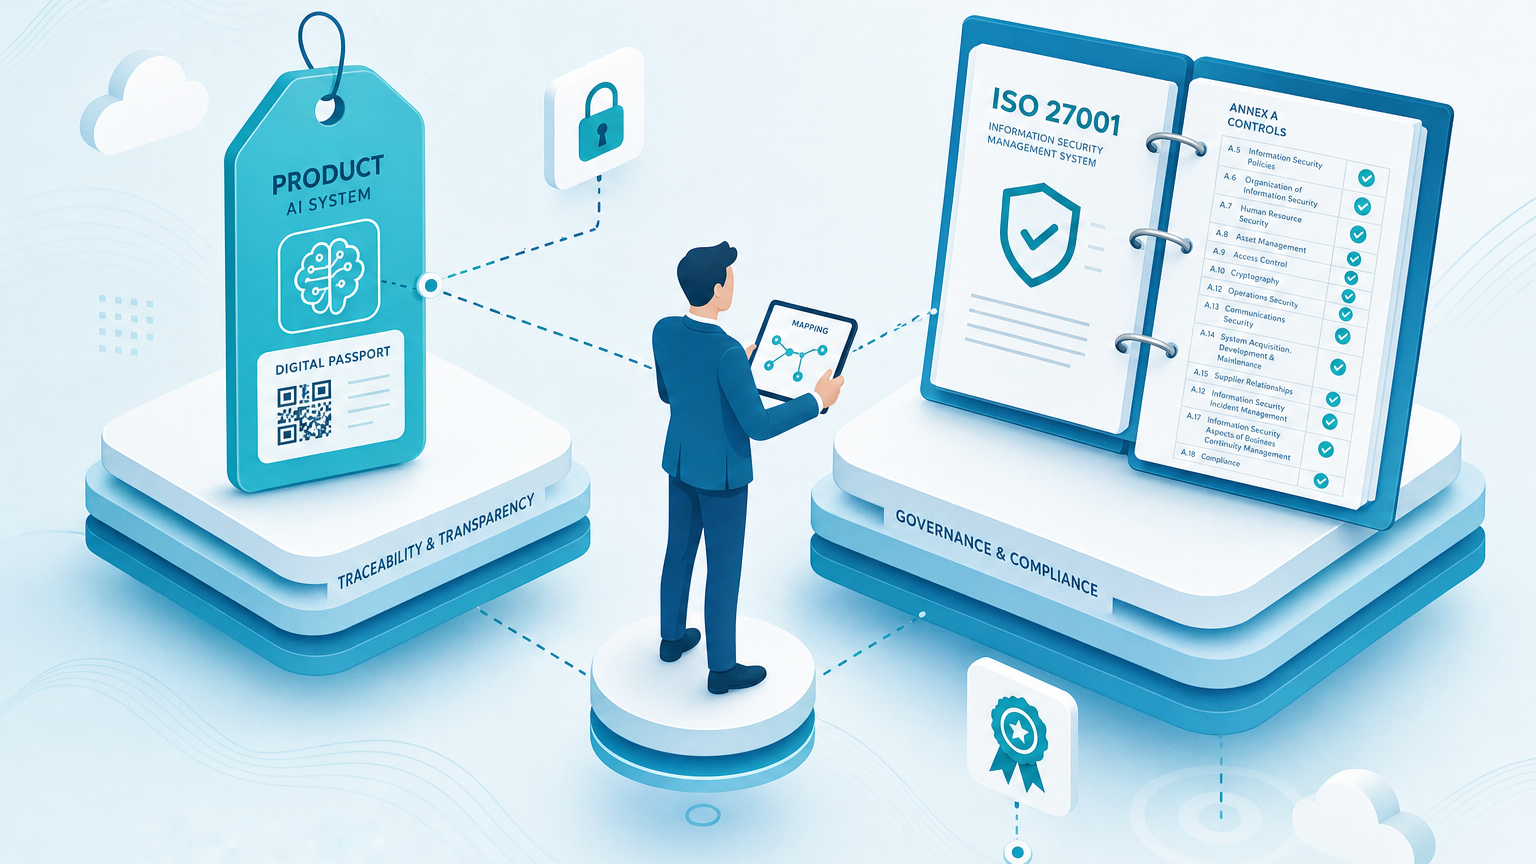
UNI at Ecomondo 2026: the new EN standards on the Digital Product Passport aren't a separate project if you already have an ISMS
CEN and CENELEC published EN 18239:2026 and EN 18246:2026 on the Digital Product Passport: with a certified ISO 27001 ISMS, it's a targeted gap analysis.
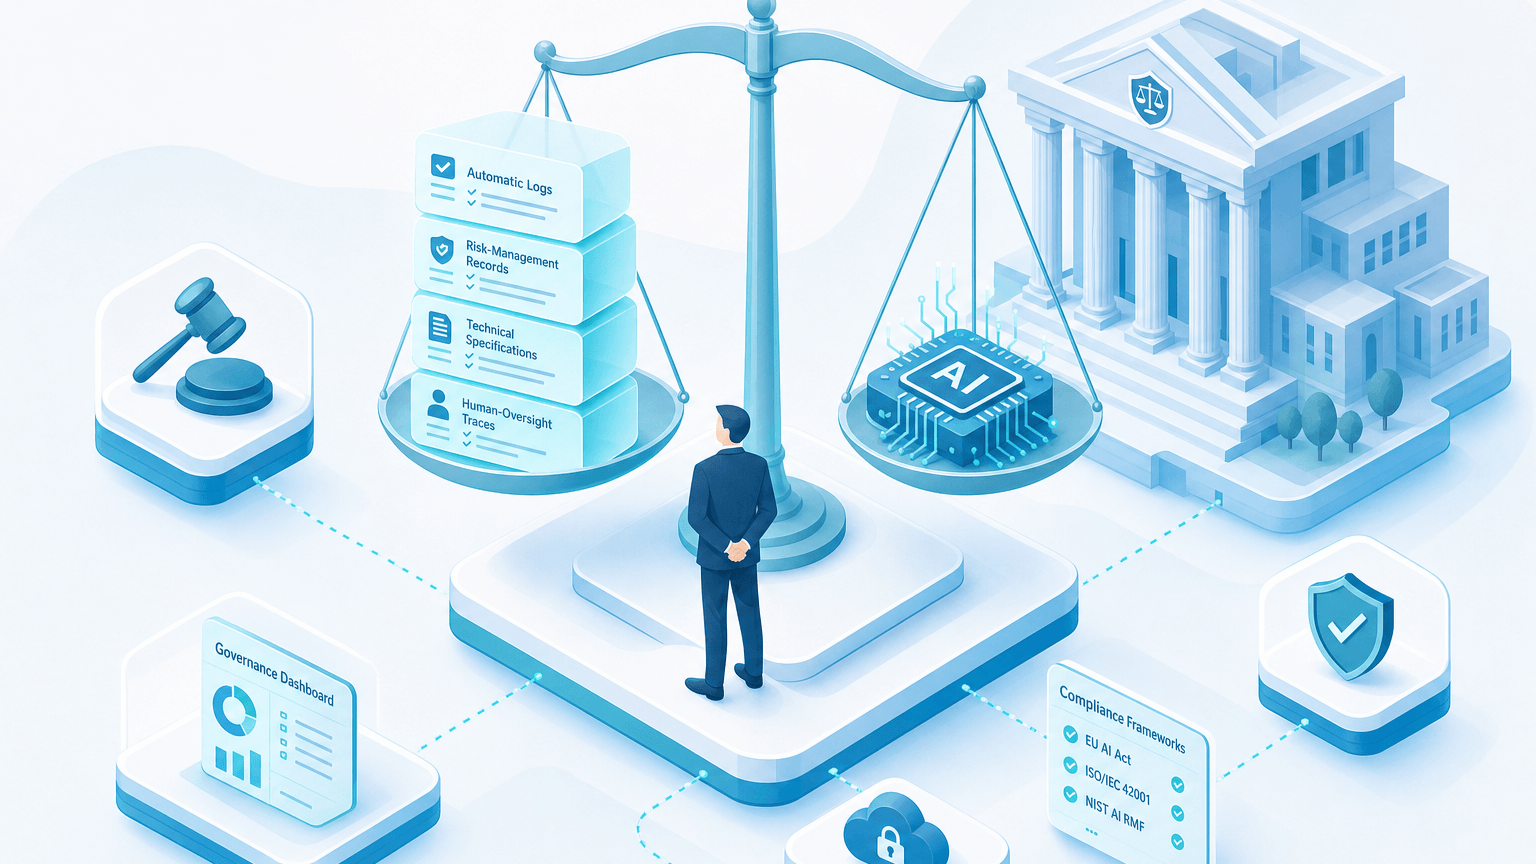
Civil liability and AI: from September 30 the burden of proof changes sides
From 30/09/2026 a judge can order disclosure of an AI system's documentation after damage. What Italy's Decree 160/2026 means and how to prepare.
Domain MCPs: Governing Data Sources for Enterprise Agents
A domain MCP doesn't "search better" than the web: it narrows the space of allowed sources. That's a governance choice for agents, not a technical detail.
AWS Bedrock: the compliance checklist before you adopt it
AWS Bedrock puts several third-party models behind one API: AWS DPA, model-provider terms, EU regions and cross-region inference — what to check first.
CNIL Fines EXTIA: The GDPR Risk Is the Process, Not the Case
CNIL fined EXTIA 300,000 EUR: of 265 erasure requests in 2024, over three quarters were mishandled or unanswered. Check your ISO 27001 A.5.34 controls.
Even DNS goes post-quantum: Cloudflare validates ML-DSA-44 on 1.1.1.1
Cloudflare validates post-quantum ML-DSA-44 DNSSEC signatures on 1.1.1.1: 2,420 bytes vs 64 for ECDSA, UDP limits and downgrade protection. A technical analysis and what it means for crypto-agility and NIS2.
ACN publishes NIS Vademecum: what changes for registration and security measures
ACN publishes the NIS Vademecum: deadlines, activity and service categorization, proportionate impact analysis. What changes for NIS2 compliance and how to align it with ISO 27001 controls.